← All features

Platforms and setup

SAP Passport and Identity Service login

SAML login into a subaccount is being deprecated, and you still need a supported way for Figaf to connect to Integration Suite.

Figaf needs access to the web APIs of SAP Cloud Integration, because they offer much more than the public APIs, and the only way to reach them is to log in as a user. Figaf used to do this with its own SAML authentication, but new SAML configurations directly into a subaccount are no longer possible, as new access has to go through SAP Cloud Identity Services. Figaf therefore supports two login options: an SAP Passport certificate and an SAP Cloud Identity Services (IAS) user. Basis and BTP administrators set this up when they connect Figaf to their tenants.

How it works

  • SAP Passport. SAP Passport is the X509 certificate you can generate yourself. Figaf suggests a separate S-user, such as figafservice@company.com, which you can use on all your SAP Integration Suite systems.
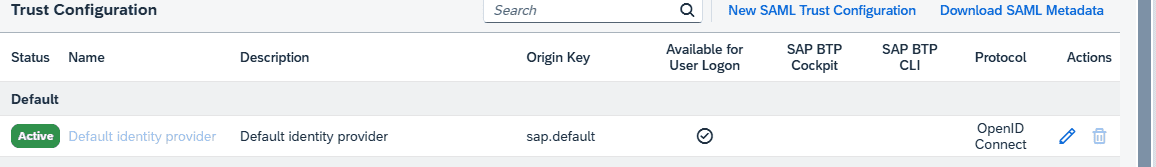
  • Roles. Give the user the roles Figaf needs: PI_Administrator, PI_Business_Expert, PI_Integration Developer and idav-content-developer.
  • Enable SAP login. For SAP Passport you must enable SAP login for the Default Identity Provider. This adds an option to the login screen, which the SAML based authentication did not.
  • Reuse the certificate. You can reuse the certificate in several agents to make setup simpler.
  • SAP Cloud Identity Services. Alternatively, create a user in SAP IAS and use it for login. You need a user with email and password that can log in with all the access needed on the Integration Suite system. It requires that you know how to set it up.
  • BTP users. Fixes for users provided by BTP that come from IAS were made in the same release.
Figaf agent configuration with SAP Passport selected as the authentication method for SAP Integration Suite
Choosing SAP Passport authentication on the agent

Business value

  • A supported connection. Both options follow SAP’s current authentication approach, so the connection between Figaf and your tenants keeps working after SAML into a subaccount is deprecated.
  • Better access control. A dedicated service user with defined roles makes it clear what Figaf can do on each tenant, and IAS users let you control access centrally.
  • Faster setup across tenants. One service user and one certificate can be reused for all your Integration Suite systems and agents.
  • Full functionality. Access to the web APIs keeps features that depend on them available, without waiting for SAP to extend the public APIs.

Good to know

  • SAP Passport login was added in release 2411 and SAP Identity Service login in release 2412. They replace the SAML authentication introduced in release 2210.
  • The login options are used when connecting the Figaf DevOps Suite, Figaf Migration Tool and Figaf B2B Management to SAP Integration Suite.

Included in

Figaf DevOps Suite

Connect Figaf to your tenants with a supported login

Use an SAP Passport certificate or an SAP Cloud Identity Services user, so Figaf can reach the Cloud Integration APIs it needs for transport, testing and monitoring.

Figaf Migration Tool

Connect the migration target tenant without SAML setup

Log on to SAP Integration Suite with an SAP Passport or an SAP Cloud Identity Services user when you connect the tenant you migrate to.

Figaf B2B Management

The same supported login for your B2B tenants

Connect the Integration Suite tenants that run TPM with an SAP Passport or an SAP Cloud Identity Services user.

See sap passport and identity service login on your landscape

No credit card required.

Integration cost calculator →

Start your free trial

No credit card required

Try Figaf DevOps Suite free for 30 days. It takes less than an hour to get started, and we send everything you need by email.

Join our newsletter

Get the latest about Figaf, SAP and anything relevant to SAP integration, every week in Figaf Weekly.